Driving IT compliance excellence
We take the stress out of your compliance journey and help you flex your security posture with our customized compliance solutions.
Standards and regulations
What we offer
We are dedicated to helping businesses navigate the complexities of regulatory requirements, ensuring that you stay compliant and focused on your core operations.
- Years of combined compliance experience
- [##]+ Placeholder
- Frameworks supported
- [##] Placeholder
- Audits and assessments supported
- [###]+ Placeholder
How we help
Three services that follow the path your auditor will take.
Compliance strategy
We assist companies in developing tailored compliance strategies to meet industry standards and regulations.
Readiness programs
We identify compliance gaps and provide strategic recommendations for a seamless compliance process.
Internal auditing
We empower your organization to uncover potential risks and streamline your path to certification with confidence.
One partner across your frameworks
Many standards share controls. We help you build once and reuse the work.
- Security SOC 2 An AICPA attestation report showing customers how you protect their data.
- Security ISO 27001 The international standard for an information security management system.
- AI ISO 42001 A management system standard for organizations that build or use AI.
- Quality ISO 9001 The international standard for quality management systems.
- Resilience ISO 22301 The international standard for business continuity management.
- Healthcare HITRUST A certifiable framework widely used across healthcare and its vendors.
- Healthcare HIPAA US rules for protecting health information.
- Federal CMMC The Department of Defense's cybersecurity requirement for its contractors.
- Federal FedRAMP The US government's security authorization program for cloud services.
- Government GovRAMP (StateRAMP) Formerly StateRAMP. A FedRAMP-style security program for state and local government.
[Client quote about working with Alameda Compliance. Two or three sentences on the outcome and what the experience was like.]
Helpful resources
All insightsArticle Placeholder
Why you should care about SOC 2
What a SOC 2 report is, why customers ask for it, and the steps to get one.
Case study Placeholder
[Placeholder] SaaS company achieves first SOC 2 Type II
Placeholder case study showing the layout. Replace with a real engagement before publishing.
Leadership
Our team consists of compliance professionals with deep expertise in IT security and certification processes. We're here to navigate the compliance maze with you, turning complex regulations into straightforward solutions, all while keeping things refreshingly human.
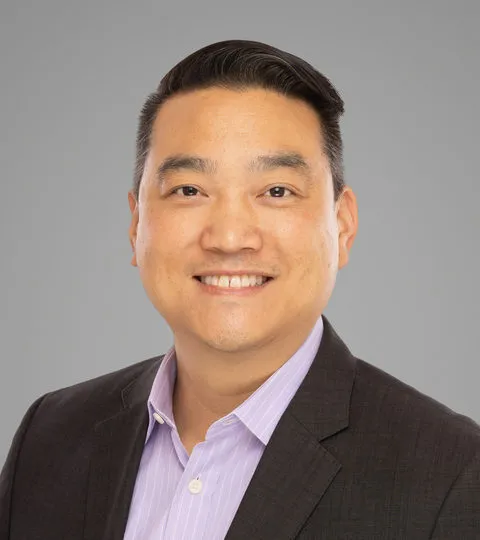
Joseph Leung
Managing Director
LinkedIn profile for Joseph Leung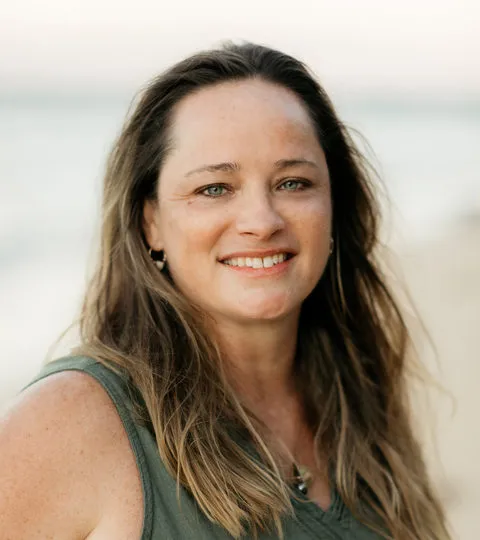
Amanda Coble
Director of Operations
LinkedIn profile for Amanda Coble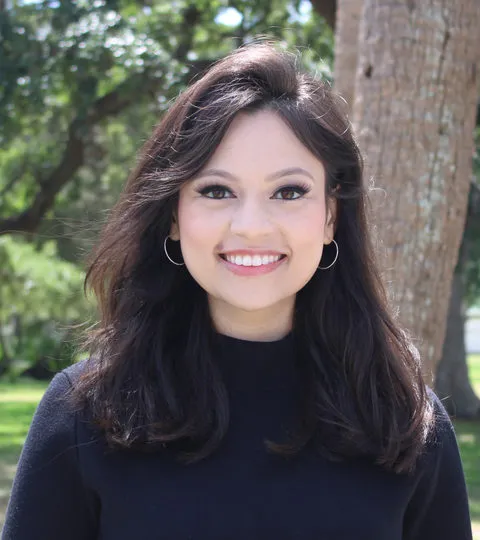
Linda Sabria
Compliance Analyst
LinkedIn profile for Linda Sabria
Let's discuss your compliance needs
Whether you're just starting your compliance journey or navigating the next steps to maintain your security posture, our team is ready to help you.